"/><stop offset="1" stop-color="rgb(96, 110, 234)"/></linearGradient><linearGradient id="W2X9EKAmH-2169866396-linear-gradient" x1="0.49751243781094523" x2="0.5024875621890548" y1="0" y2="1"><stop offset="0" stop-color="rgb(120, 70, 175)"/><stop offset="1" stop-color="rgb(96, 110, 234)"/></linearGradient></defs><g fill="transparent" height="6.667790173290786px" id="WxDMP_wo5" transform="translate(0 -0.335)" width="40.000237191183544px"><path d="M 0 6.667 L 0 0 L 40 0 L 40 6.667 Z" fill="transparent" height="6.666666666666666px" id="sESj6aK3L" width="40px"/><path d="M 5.133 1.25 L 5.133 4.583 L 2.933 5.833 L 0.733 4.583 L 0.733 2.083 L 2.933 0.833 L 2.933 0 L 0 1.667 L 0 5 L 2.933 6.667 L 5.867 5 L 5.867 1.667 Z" fill="url(%23SjiByaea2-2169866396-linear-gradient)" height="6.666666666666666px" id="SjiByaea2" width="5.866783625730994px"/><path d="M 0.733 3.333 L 0.733 2.5 L 1.467 2.083 L 1.467 1.25 L 0 2.083 L 0 3.75 L 1.467 4.583 L 2.933 3.75 L 2.933 0.417 L 2.2 0 L 2.2 3.333 L 1.467 3.75 Z" fill="url(%23W2X9EKAmH-2169866396-linear-gradient)" height="4.583333333333334px" id="W2X9EKAmH" transform="translate(1.467 0.417)" width="2.9334035087719315px"/><path d="M 0 3.985 L 0 0 L 1.547 0 C 1.864 0 2.128 0.045 2.342 0.134 C 2.559 0.22 2.733 0.346 2.864 0.513 C 2.994 0.681 3.087 0.883 3.142 1.12 C 3.201 1.357 3.231 1.628 3.231 1.931 C 3.231 2.239 3.203 2.517 3.148 2.766 C 3.097 3.014 3.008 3.23 2.881 3.413 C 2.755 3.596 2.585 3.738 2.371 3.839 C 2.158 3.936 1.891 3.985 1.571 3.985 Z M 0.818 3.308 L 1.524 3.308 C 1.709 3.308 1.86 3.273 1.974 3.203 C 2.089 3.133 2.176 3.036 2.235 2.911 C 2.298 2.783 2.34 2.637 2.36 2.474 C 2.383 2.307 2.395 2.126 2.395 1.931 C 2.395 1.745 2.383 1.575 2.36 1.424 C 2.336 1.268 2.292 1.136 2.229 1.027 C 2.17 0.914 2.083 0.829 1.968 0.77 C 1.858 0.708 1.709 0.677 1.524 0.677 L 0.818 0.677 Z" fill="rgb(255, 255, 255)" height="3.984970760233911px" id="pQ_u90pAO" transform="translate(8.945 1.452)" width="3.231064327485413px"/><path d="M 0 2.999 L 0 0.07 L 0.789 0.07 L 0.789 0.414 C 0.856 0.364 0.939 0.311 1.038 0.257 C 1.136 0.198 1.243 0.146 1.358 0.099 C 1.476 0.049 1.589 0.016 1.696 0 L 1.696 0.753 C 1.593 0.768 1.484 0.795 1.37 0.834 C 1.255 0.869 1.146 0.908 1.044 0.951 C 0.945 0.994 0.86 1.033 0.789 1.068 L 0.789 2.999 Z" fill="rgb(255, 255, 255)" height="2.9989356725146212px" id="HUQJBJ1t7" transform="translate(12.803 2.437)" width="1.6956725146198863px"/><path d="M 1.387 3.057 C 1.051 3.057 0.781 3.003 0.575 2.894 C 0.373 2.785 0.227 2.618 0.136 2.392 C 0.045 2.163 0 1.867 0 1.505 C 0 1.155 0.047 0.871 0.142 0.653 C 0.237 0.432 0.387 0.268 0.593 0.163 C 0.798 0.054 1.063 0 1.387 0 C 1.715 0 1.98 0.054 2.182 0.163 C 2.387 0.268 2.537 0.432 2.632 0.653 C 2.731 0.871 2.78 1.155 2.78 1.505 C 2.78 1.867 2.735 2.163 2.644 2.392 C 2.553 2.618 2.405 2.785 2.2 2.894 C 1.998 3.003 1.727 3.057 1.387 3.057 Z M 1.387 2.415 C 1.553 2.415 1.678 2.386 1.761 2.328 C 1.844 2.266 1.899 2.168 1.927 2.036 C 1.958 1.9 1.974 1.723 1.974 1.505 C 1.974 1.291 1.956 1.122 1.921 0.998 C 1.885 0.869 1.826 0.778 1.743 0.723 C 1.66 0.669 1.541 0.642 1.387 0.642 C 1.237 0.642 1.118 0.669 1.032 0.723 C 0.949 0.778 0.889 0.869 0.854 0.998 C 0.818 1.122 0.8 1.291 0.8 1.505 C 0.8 1.723 0.814 1.9 0.842 2.036 C 0.873 2.168 0.931 2.266 1.014 2.328 C 1.097 2.386 1.221 2.415 1.387 2.415 Z" fill="rgb(255, 255, 255)" height="3.057263157894756px" id="EIrO2_THA" transform="translate(14.828 2.444)" width="2.7804678362573156px"/><path d="M 0 4.224 L 0 0.064 L 0.782 0.064 L 0.788 0.251 C 0.844 0.216 0.913 0.179 0.996 0.14 C 1.083 0.101 1.176 0.068 1.275 0.041 C 1.373 0.014 1.47 0 1.565 0 C 1.964 0 2.251 0.126 2.425 0.379 C 2.599 0.628 2.686 1.007 2.686 1.517 C 2.686 1.883 2.642 2.178 2.555 2.404 C 2.468 2.629 2.328 2.795 2.134 2.9 C 1.945 3.005 1.694 3.057 1.381 3.057 C 1.282 3.057 1.176 3.049 1.061 3.034 C 0.947 3.018 0.856 3.003 0.788 2.987 L 0.788 4.224 Z M 1.257 2.41 C 1.415 2.41 1.539 2.377 1.63 2.31 C 1.721 2.244 1.784 2.145 1.82 2.013 C 1.86 1.877 1.879 1.706 1.879 1.499 C 1.879 1.181 1.834 0.961 1.743 0.84 C 1.656 0.716 1.529 0.653 1.364 0.653 C 1.3 0.653 1.233 0.661 1.162 0.677 C 1.091 0.692 1.022 0.712 0.954 0.735 C 0.887 0.758 0.832 0.782 0.788 0.805 L 0.788 2.369 C 0.836 2.373 0.903 2.38 0.99 2.392 C 1.081 2.404 1.17 2.41 1.257 2.41 Z" fill="rgb(255, 255, 255)" height="4.2241871345029445px" id="azBGUfGeg" transform="translate(18.207 2.444)" width="2.6856140350876103px"/><path d="M 0 2.929 L 0 2.27 L 1.346 0.688 L 0 0.688 L 0 0 L 2.384 0 L 2.384 0.636 L 1.026 2.24 L 2.389 2.24 L 2.389 2.929 Z" fill="rgb(255, 255, 255)" height="2.9289239766081856px" id="GMxU4HuKZ" transform="translate(21.361 2.507)" width="2.3893567251462002px"/><path d="M 1.387 3.057 C 1.051 3.057 0.781 3.003 0.575 2.894 C 0.374 2.785 0.227 2.618 0.136 2.392 C 0.045 2.163 0 1.867 0 1.505 C 0 1.155 0.047 0.871 0.142 0.653 C 0.237 0.432 0.387 0.268 0.593 0.163 C 0.798 0.054 1.063 0 1.387 0 C 1.715 0 1.98 0.054 2.182 0.163 C 2.387 0.268 2.537 0.432 2.632 0.653 C 2.731 0.871 2.78 1.155 2.78 1.505 C 2.78 1.867 2.735 2.163 2.644 2.392 C 2.553 2.618 2.405 2.785 2.2 2.894 C 1.998 3.003 1.727 3.057 1.387 3.057 Z M 1.387 2.415 C 1.553 2.415 1.678 2.386 1.761 2.328 C 1.844 2.266 1.899 2.168 1.927 2.036 C 1.958 1.9 1.974 1.723 1.974 1.505 C 1.974 1.291 1.956 1.122 1.921 0.998 C 1.885 0.869 1.826 0.778 1.743 0.723 C 1.66 0.669 1.541 0.642 1.387 0.642 C 1.237 0.642 1.118 0.669 1.031 0.723 C 0.949 0.778 0.889 0.869 0.854 0.998 C 0.818 1.122 0.8 1.291 0.8 1.505 C 0.8 1.723 0.814 1.9 0.842 2.036 C 0.874 2.168 0.931 2.266 1.014 2.328 C 1.097 2.386 1.221 2.415 1.387 2.415 Z" fill="rgb(255, 255, 255)" height="3.057263157894756px" id="hVOAJWBR_" transform="translate(24.216 2.444)" width="2.7804678362571735px"/><path d="M 0 2.993 L 0 0.064 L 0.789 0.064 L 0.789 0.251 C 0.852 0.212 0.929 0.175 1.02 0.14 C 1.111 0.101 1.205 0.068 1.304 0.041 C 1.407 0.014 1.506 0 1.601 0 C 1.877 0 2.091 0.049 2.241 0.146 C 2.395 0.239 2.504 0.395 2.567 0.613 C 2.63 0.827 2.662 1.114 2.662 1.476 L 2.662 2.993 L 1.867 2.993 L 1.867 1.517 C 1.867 1.315 1.855 1.153 1.832 1.033 C 1.808 0.908 1.763 0.819 1.695 0.764 C 1.628 0.71 1.529 0.683 1.399 0.683 C 1.328 0.683 1.253 0.69 1.174 0.706 C 1.099 0.718 1.026 0.735 0.954 0.758 C 0.887 0.782 0.832 0.805 0.789 0.828 L 0.789 2.993 Z" fill="rgb(255, 255, 255)" height="2.993099415204677px" id="k6aC5HsJY" transform="translate(27.596 2.444)" width="2.6617543859649118px"/><path d="M 1.316 3.057 C 0.988 3.057 0.727 3.003 0.533 2.894 C 0.344 2.785 0.207 2.62 0.124 2.398 C 0.042 2.176 0 1.898 0 1.564 C 0 1.202 0.051 0.906 0.154 0.677 C 0.261 0.447 0.415 0.278 0.616 0.169 C 0.818 0.056 1.067 0 1.363 0 C 1.802 0 2.132 0.109 2.353 0.327 C 2.579 0.545 2.691 0.889 2.691 1.359 L 2.656 1.791 L 0.794 1.791 C 0.798 2.009 0.844 2.172 0.931 2.281 C 1.018 2.39 1.168 2.445 1.381 2.445 C 1.504 2.445 1.638 2.443 1.784 2.439 C 1.931 2.431 2.075 2.423 2.217 2.415 C 2.363 2.408 2.488 2.4 2.591 2.392 L 2.609 2.935 C 2.51 2.95 2.385 2.968 2.235 2.987 C 2.085 3.007 1.929 3.022 1.767 3.034 C 1.609 3.049 1.458 3.057 1.316 3.057 Z M 0.794 1.295 L 1.903 1.295 C 1.903 1.031 1.86 0.846 1.773 0.741 C 1.69 0.636 1.553 0.583 1.363 0.583 C 1.178 0.583 1.035 0.638 0.937 0.747 C 0.842 0.856 0.794 1.039 0.794 1.295 Z" fill="rgb(255, 255, 255)" height="3.0572631578947593px" id="HWRgQ4Zqc" transform="translate(30.819 2.443)" width="2.691461988304269px"/><path d="M 0 3.985 L 1.031 0 L 2.46 0 L 3.486 3.985 L 2.668 3.985 L 2.442 3.18 L 1.026 3.18 L 0.812 3.985 Z M 1.156 2.532 L 2.324 2.532 L 1.867 0.653 L 1.619 0.653 Z" fill="rgb(255, 255, 255)" height="3.984970760233911px" id="FKU8sIkPM" transform="translate(35.19 1.452)" width="3.48608187134505px"/><path d="M 0 3.985 L 0 0 L 0.818 0 L 0.818 3.985 Z" fill="rgb(255, 255, 255)" height="3.984970760233918px" id="dMjn7rx8Q" transform="translate(39.182 1.452)" width="1px"/></g></svg>)

SIEMs excel at collecting data, correlating events, and raising alerts, but their capabilities end at detection. Once an alert fires, analysts must still dig through email logs, endpoint data, and identity systems to determine what really happened. Dropzone AI fills that gap by automatically pulling in the missing context, investigating across systems, and explaining what’s actually going on, all without requiring scripts, playbooks, or full data ingestion. In this article, we’ll look at how Dropzone AI transforms a traditional SIEM into a system that can think, reason, and respond on its own.
Why Can’t SIEMs Investigate Alerts on Their Own?
What Context Do SIEMs Typically Miss?
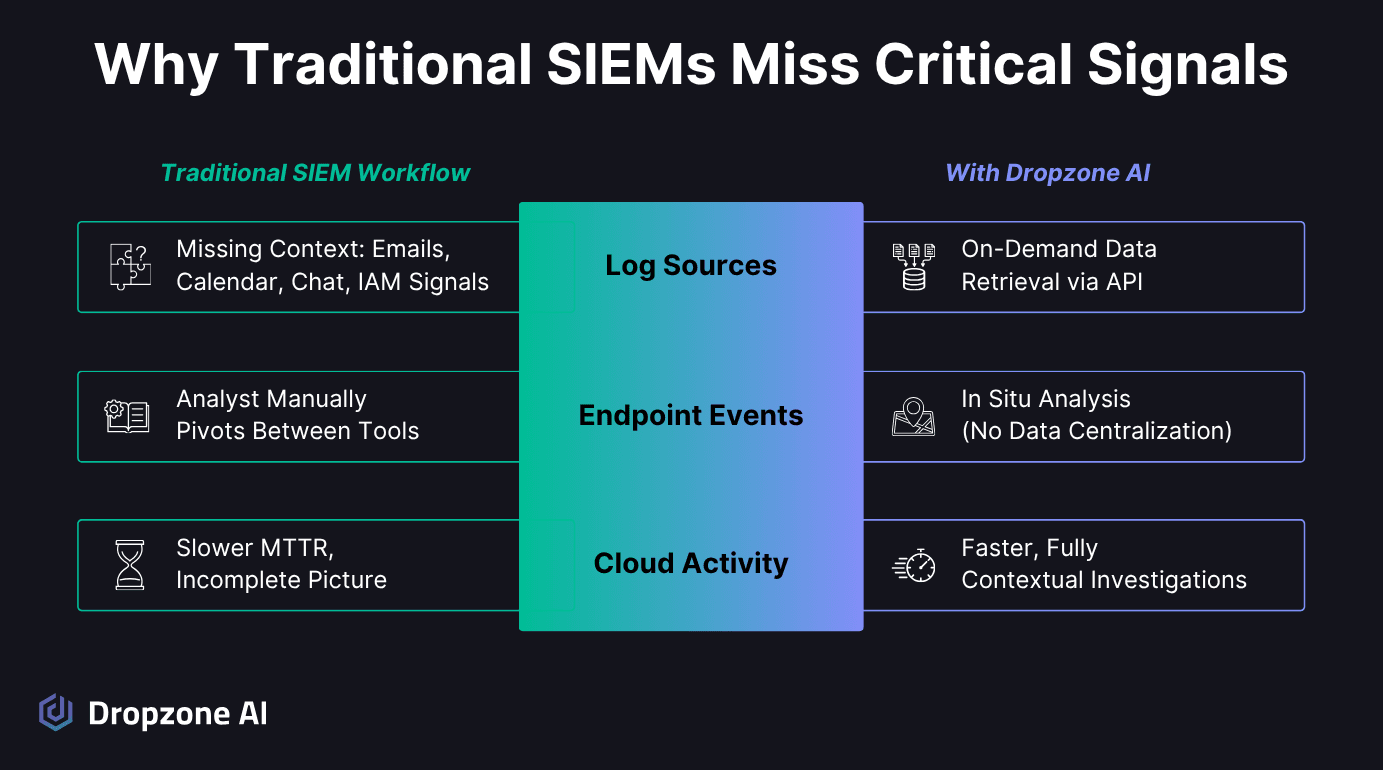
SIEMs excel at capturing system data, such as firewalls, endpoints, and authentication events, but often overlook significant human context. High-volume sources, such as SaaS logs, often remain outside the SIEM due to their high cost and complexity in ingestion. In addition, there’s some data crucial to investigations that the SIEM doesn’t have access to, such as email and calendar events. That means analysts see the alert but not the situation around it. They know something happened, but need to understand why.
Context sources typically outside SIEM:
Email contents and communications patterns
Contents of shared files
Collaboration tool usage
Calendar schedules
SaaS application activity
Cloud service logs
When that happens, analysts do a lot of investigative legwork, using multiple tools to piece things together. They jump between consoles, export logs, and manually cross-check timestamps. It’s slow, repetitive work that eats into response time and increases the chance of missing key details. Most of the time, the data they need is already available; it’s just locked in systems that the SIEM doesn’t access.
How Dropzone AI Brings the Missing Context Back
Dropzone AI fills in those gaps without changing how the SIEM works by connecting through secure, read-only APIs and pulling missing context, like meeting activity or recent login details, or reading through email contents and shared files. Dropzone AI can also use tools for things like PDF analysis and sandbox execution.
You don’t need to send more data to the SIEM for analysis; Dropzone AI goes out and finds the needed context itself. Every Dropzone AI request to a data source is logged under strict access controls. Under the hood, Dropzone AI uses pre-trained AI agents that each specialize in a specific type of tool or skill.
The video below explains how Dropzone AI reasons through an investigation:
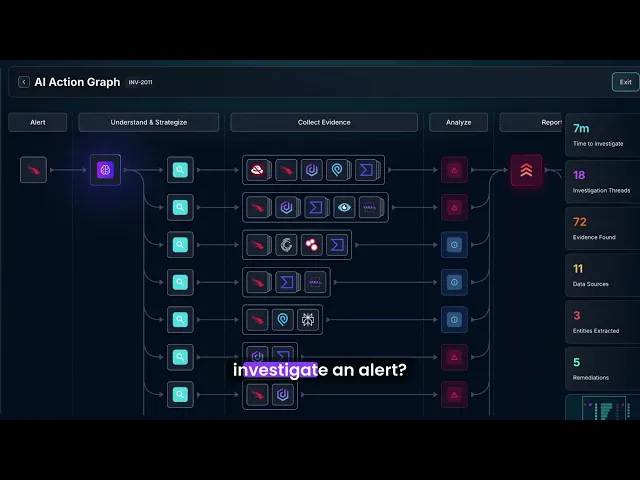
When an SIEM alert appears, Dropzone AI determines what’s missing, queries the appropriate sources, and reasons through the evidence to reach a verdict—an alert is either a true or false positive, malicious or benign. Analysts get a full picture of what happened in minutes, eliminating the need for manual digging.
What’s the Difference Between SOAR Automation and AI Investigation?
How SOAR Works with AI SOC Analysts
Many security leaders and architects have questions about where SOAR fits with AI SOC analysts. In fact, the two technologies are complementary.
SOAR platforms excel at handling repetitive tasks, enriching alerts, isolating hosts, or closing tickets, but their capabilities are limited to what’s already been scripted. Every action follows a predefined rule or decision tree.
SOAR capabilities:
Executes predefined workflows
Automates repetitive tasks
Requires playbook maintenance
AI investigation capabilities:
Reasons through ambiguous evidence
Adapts to unknown threats
Explains findings with context
When a new or ambiguous SIEM alert appears, SOAR can’t adapt; it either stalls or routes it back to a human analyst. That means complex, unfamiliar attacks often slip through the automation layer and land in the manual queue.
Analysts often spend time on investigation steps that could be automated if the system were capable of reasoning. They still need to identify intent, compare behavior across systems, and create timelines to explain what actually happened. SOAR handles execution, not interpretation. It doesn’t learn from previous investigations or adjust based on uncertainty. That’s where AI-driven analysis changes what’s possible in a SOC.
How Dropzone AI Thinks Like an Expert Analyst
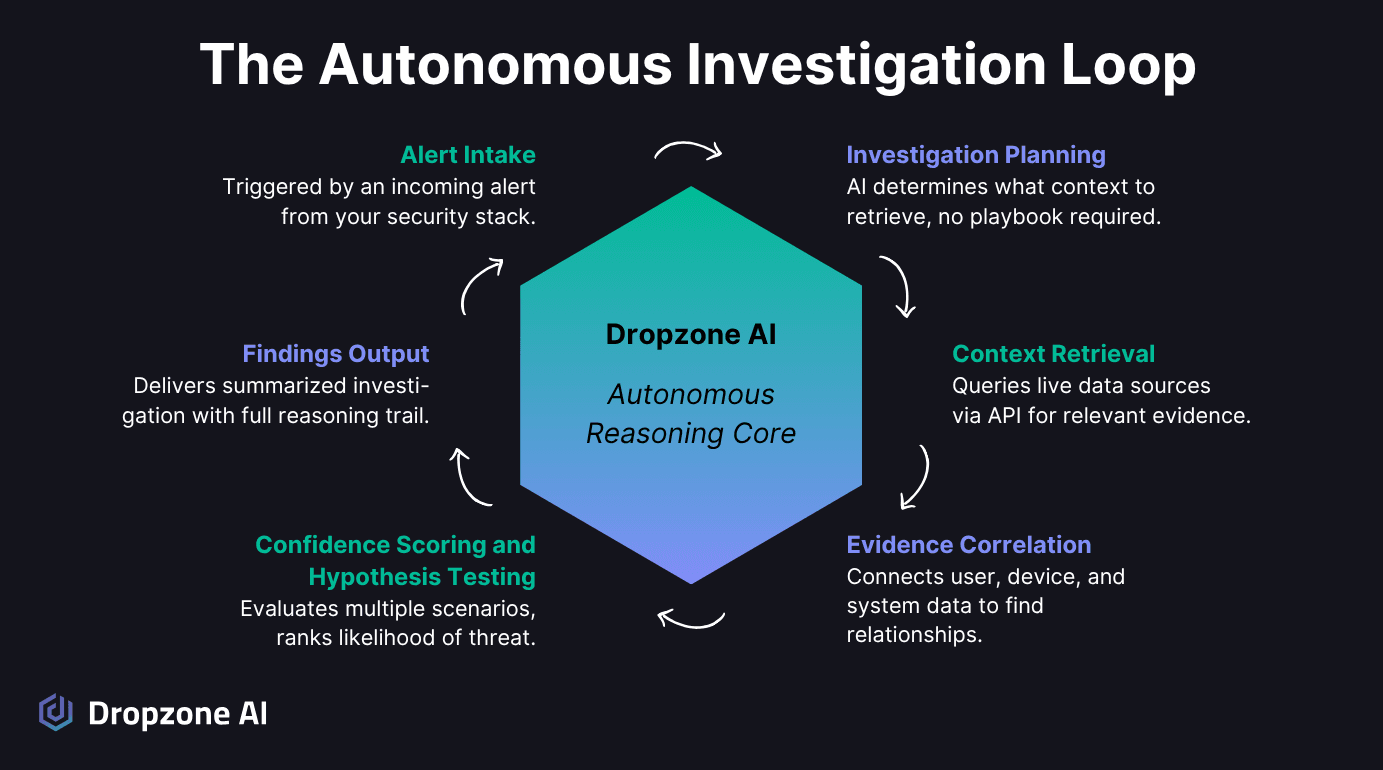
Dropzone AI is an agentic system that uses large language models and context memory to go beyond rule-based automation. Instead of following a static playbook, it learns how to reason through evidence.
When a SIEM alert arrives in the queue, Dropzone AI automatically gathers data from endpoints, IAM logs, mailboxes, shared files, historical login activity, calendar events, VPN activity—the list of investigative context it gathers goes on. Dropzone AI can even interview users when needed. It compares these signals, looks for patterns of intent, and builds a contextual timeline of the event, all within minutes.
The system forms hypotheses about why an alert might be malicious or benign, weighs them against the context gathered, and then presents a conclusion with supporting evidence. That report includes the logic behind its conclusion, why it decided something was benign, suspicious, or worth escalation.
From there, Dropzone AI can send its findings directly into a SOAR for response automation or ticketing system for review. Analysts don’t just get an alert; they get a full, reasoned investigation ready to dismiss or escalate.
How Does Dropzone AI Work With Your Existing Security Stack?

From Alert Overload to Interesting Security Work
Working in a SOC, you know how reactive things can feel. The SIEM lights up with alerts and analysts scramble to piece together what’s real and what’s noise.
Each investigation means jumping between console endpoint logs, email evidence, and identity records, hoping the full story eventually comes together. It’s exhausting, and honestly, it’s not the best use of human time.
Dropzone AI changes that dynamic; when an alert hits, it immediately starts collecting context from across your connected systems. It checks user sessions, endpoint activity, and communication patterns, then stitches it all together into a clear, readable summary.
What used to take hours of manual digging now happens automatically. Analysts can focus on confirming and making decisions, rather than chasing data.
Fits Right Into the Tools You Already Use
Dropzone AI doesn’t replace your stack; it works alongside it; it connects through simple REST APIs or webhooks, allowing alerts from your SIEM to flow directly into Dropzone AI’s investigation engine. Dropzone AI also queries your SIEM like an expert user to gather data needed for an investigation.
Integration approach:
Connects via REST APIs, webhooks, or MCP
Read-only access with audit logging
No data storage or ingestion required
Works alongside existing tools
There’s no big deployment project or architecture change required. Everything runs as a separate service that uses the same security boundaries you already have in place.
Every query Dropzone AI makes is permission-bound, logged, and traceable. It operates with role-based access and strict rate limits, so nothing slips outside of policy.
All the heavy lifting happens in memory, with no extra storage or ingestion required. You get richer insights without adding new infrastructure or data pipelines. It just helps your existing tools work smarter together.
Results Your Team Can Actually Feel
The difference is easy to notice. Instead of triaging a small subset of cut-and-dry alerts, Dropzone AI helps your team cover much more, including endpoint, cloud, identity, network, and insider threat alerts. It handles the repetitive, low-level work, then delivers organized, evidence-based findings for analysts to review. Investigations move faster, fatigue decreases, and confidence in decisions increases.
You’ll see it in the numbers: shorter mean time to resolution, fewer missed alerts, and cleaner escalations. But you’ll also feel it in the workflow. Your analysts regain their time, your SOC becomes calmer, and the team can finally focus on strategic security thinking instead of just keeping up with alerts.
What Systems Does Dropzone AI Connect To?
Data sources accessed during investigation:
Email systems (Microsoft 365, Google Workspace)
Identity providers (Okta, Active Directory)
Endpoint platforms (CrowdStrike, SentinelOne)
Cloud infrastructure (AWS, Azure, GCP)
VPN and network access logs
SaaS applications and collaboration tools
Security approach: All connections use read-only API access with full audit logging and role-based permissions.
Key Takeaways
SIEMs Don’t See the Full Picture. Traditional SIEMs collect valuable logs but miss critical human-layer context, such as email, calendar, and SaaS activity, creating investigation blind spots that slow down response.
Dropzone AI Investigates, Not Just Automates. Unlike SOAR tools that follow rigid playbooks, Dropzone AI uses AI reasoning to gather context, form hypotheses, and explain findings, turning alerts into clear, evidence-backed insights.
Smarter Workflows, Not More Tools. Dropzone AI runs alongside your existing SIEM, automating triage and investigation without changing your infrastructure. Analysts gain speed, coverage, and clarity without extra complexity.
Conclusion
SIEMs are incredible at detection, but detection is only half of the equation. Without automated investigation that can pull context from across your entire environment and reason to a conclusion, alerts pile up, analysts burn out, and threats slip through.
Dropzone AI changes that. It turns your SIEM into a thinking system—one that doesn’t just flag suspicious activity, but autonomously investigates it with the skill and reasoning of a senior analyst. Your team gets complete, evidence-backed answers instead of ambiguous alerts, freeing them to focus on high-impact work that requires human judgment.
See Dropzone AI in Action
Ready to see how AI investigation transforms your SIEM workflow? Our self-guided demo lets you experience Dropzone AI autonomously investigating real security alerts in a live environment.
What you’ll see in the demo:
Complete alert investigations in 3-10 minutes
Automatic context gathering from email, identity, and cloud systems
AI reasoning that explains findings with supporting evidence
Integration with your existing SIEM and security stack
No sales call required. Explore the platform at your own pace and see exactly how Dropzone AI turns your SIEM alerts into actionable insights.
" width="32px"><path d="M 10 11.4 L 0 1.4 L 1.4 0 L 10 8.6 L 18.6 0 L 20 1.4 Z" fill="rgb(0, 0, 0)" height="11.400000000000006px" id="WzVcCPzSg" transform="translate(6 10.5)" width="20px"/><path d="M 0 0 L 32 0 L 32 32 L 0 32 Z" fill="transparent" height="32px" id="JnWsCmB6z" width="32px"/></g></svg>)