"/><stop offset="1" stop-color="rgb(96, 110, 234)"/></linearGradient><linearGradient id="W2X9EKAmH-2169866396-linear-gradient" x1="0.49751243781094523" x2="0.5024875621890548" y1="0" y2="1"><stop offset="0" stop-color="rgb(120, 70, 175)"/><stop offset="1" stop-color="rgb(96, 110, 234)"/></linearGradient></defs><g fill="transparent" height="6.667790173290786px" id="WxDMP_wo5" transform="translate(0 -0.335)" width="40.000237191183544px"><path d="M 0 6.667 L 0 0 L 40 0 L 40 6.667 Z" fill="transparent" height="6.666666666666666px" id="sESj6aK3L" width="40px"/><path d="M 5.133 1.25 L 5.133 4.583 L 2.933 5.833 L 0.733 4.583 L 0.733 2.083 L 2.933 0.833 L 2.933 0 L 0 1.667 L 0 5 L 2.933 6.667 L 5.867 5 L 5.867 1.667 Z" fill="url(%23SjiByaea2-2169866396-linear-gradient)" height="6.666666666666666px" id="SjiByaea2" width="5.866783625730994px"/><path d="M 0.733 3.333 L 0.733 2.5 L 1.467 2.083 L 1.467 1.25 L 0 2.083 L 0 3.75 L 1.467 4.583 L 2.933 3.75 L 2.933 0.417 L 2.2 0 L 2.2 3.333 L 1.467 3.75 Z" fill="url(%23W2X9EKAmH-2169866396-linear-gradient)" height="4.583333333333334px" id="W2X9EKAmH" transform="translate(1.467 0.417)" width="2.9334035087719315px"/><path d="M 0 3.985 L 0 0 L 1.547 0 C 1.864 0 2.128 0.045 2.342 0.134 C 2.559 0.22 2.733 0.346 2.864 0.513 C 2.994 0.681 3.087 0.883 3.142 1.12 C 3.201 1.357 3.231 1.628 3.231 1.931 C 3.231 2.239 3.203 2.517 3.148 2.766 C 3.097 3.014 3.008 3.23 2.881 3.413 C 2.755 3.596 2.585 3.738 2.371 3.839 C 2.158 3.936 1.891 3.985 1.571 3.985 Z M 0.818 3.308 L 1.524 3.308 C 1.709 3.308 1.86 3.273 1.974 3.203 C 2.089 3.133 2.176 3.036 2.235 2.911 C 2.298 2.783 2.34 2.637 2.36 2.474 C 2.383 2.307 2.395 2.126 2.395 1.931 C 2.395 1.745 2.383 1.575 2.36 1.424 C 2.336 1.268 2.292 1.136 2.229 1.027 C 2.17 0.914 2.083 0.829 1.968 0.77 C 1.858 0.708 1.709 0.677 1.524 0.677 L 0.818 0.677 Z" fill="rgb(255, 255, 255)" height="3.984970760233911px" id="pQ_u90pAO" transform="translate(8.945 1.452)" width="3.231064327485413px"/><path d="M 0 2.999 L 0 0.07 L 0.789 0.07 L 0.789 0.414 C 0.856 0.364 0.939 0.311 1.038 0.257 C 1.136 0.198 1.243 0.146 1.358 0.099 C 1.476 0.049 1.589 0.016 1.696 0 L 1.696 0.753 C 1.593 0.768 1.484 0.795 1.37 0.834 C 1.255 0.869 1.146 0.908 1.044 0.951 C 0.945 0.994 0.86 1.033 0.789 1.068 L 0.789 2.999 Z" fill="rgb(255, 255, 255)" height="2.9989356725146212px" id="HUQJBJ1t7" transform="translate(12.803 2.437)" width="1.6956725146198863px"/><path d="M 1.387 3.057 C 1.051 3.057 0.781 3.003 0.575 2.894 C 0.373 2.785 0.227 2.618 0.136 2.392 C 0.045 2.163 0 1.867 0 1.505 C 0 1.155 0.047 0.871 0.142 0.653 C 0.237 0.432 0.387 0.268 0.593 0.163 C 0.798 0.054 1.063 0 1.387 0 C 1.715 0 1.98 0.054 2.182 0.163 C 2.387 0.268 2.537 0.432 2.632 0.653 C 2.731 0.871 2.78 1.155 2.78 1.505 C 2.78 1.867 2.735 2.163 2.644 2.392 C 2.553 2.618 2.405 2.785 2.2 2.894 C 1.998 3.003 1.727 3.057 1.387 3.057 Z M 1.387 2.415 C 1.553 2.415 1.678 2.386 1.761 2.328 C 1.844 2.266 1.899 2.168 1.927 2.036 C 1.958 1.9 1.974 1.723 1.974 1.505 C 1.974 1.291 1.956 1.122 1.921 0.998 C 1.885 0.869 1.826 0.778 1.743 0.723 C 1.66 0.669 1.541 0.642 1.387 0.642 C 1.237 0.642 1.118 0.669 1.032 0.723 C 0.949 0.778 0.889 0.869 0.854 0.998 C 0.818 1.122 0.8 1.291 0.8 1.505 C 0.8 1.723 0.814 1.9 0.842 2.036 C 0.873 2.168 0.931 2.266 1.014 2.328 C 1.097 2.386 1.221 2.415 1.387 2.415 Z" fill="rgb(255, 255, 255)" height="3.057263157894756px" id="EIrO2_THA" transform="translate(14.828 2.444)" width="2.7804678362573156px"/><path d="M 0 4.224 L 0 0.064 L 0.782 0.064 L 0.788 0.251 C 0.844 0.216 0.913 0.179 0.996 0.14 C 1.083 0.101 1.176 0.068 1.275 0.041 C 1.373 0.014 1.47 0 1.565 0 C 1.964 0 2.251 0.126 2.425 0.379 C 2.599 0.628 2.686 1.007 2.686 1.517 C 2.686 1.883 2.642 2.178 2.555 2.404 C 2.468 2.629 2.328 2.795 2.134 2.9 C 1.945 3.005 1.694 3.057 1.381 3.057 C 1.282 3.057 1.176 3.049 1.061 3.034 C 0.947 3.018 0.856 3.003 0.788 2.987 L 0.788 4.224 Z M 1.257 2.41 C 1.415 2.41 1.539 2.377 1.63 2.31 C 1.721 2.244 1.784 2.145 1.82 2.013 C 1.86 1.877 1.879 1.706 1.879 1.499 C 1.879 1.181 1.834 0.961 1.743 0.84 C 1.656 0.716 1.529 0.653 1.364 0.653 C 1.3 0.653 1.233 0.661 1.162 0.677 C 1.091 0.692 1.022 0.712 0.954 0.735 C 0.887 0.758 0.832 0.782 0.788 0.805 L 0.788 2.369 C 0.836 2.373 0.903 2.38 0.99 2.392 C 1.081 2.404 1.17 2.41 1.257 2.41 Z" fill="rgb(255, 255, 255)" height="4.2241871345029445px" id="azBGUfGeg" transform="translate(18.207 2.444)" width="2.6856140350876103px"/><path d="M 0 2.929 L 0 2.27 L 1.346 0.688 L 0 0.688 L 0 0 L 2.384 0 L 2.384 0.636 L 1.026 2.24 L 2.389 2.24 L 2.389 2.929 Z" fill="rgb(255, 255, 255)" height="2.9289239766081856px" id="GMxU4HuKZ" transform="translate(21.361 2.507)" width="2.3893567251462002px"/><path d="M 1.387 3.057 C 1.051 3.057 0.781 3.003 0.575 2.894 C 0.374 2.785 0.227 2.618 0.136 2.392 C 0.045 2.163 0 1.867 0 1.505 C 0 1.155 0.047 0.871 0.142 0.653 C 0.237 0.432 0.387 0.268 0.593 0.163 C 0.798 0.054 1.063 0 1.387 0 C 1.715 0 1.98 0.054 2.182 0.163 C 2.387 0.268 2.537 0.432 2.632 0.653 C 2.731 0.871 2.78 1.155 2.78 1.505 C 2.78 1.867 2.735 2.163 2.644 2.392 C 2.553 2.618 2.405 2.785 2.2 2.894 C 1.998 3.003 1.727 3.057 1.387 3.057 Z M 1.387 2.415 C 1.553 2.415 1.678 2.386 1.761 2.328 C 1.844 2.266 1.899 2.168 1.927 2.036 C 1.958 1.9 1.974 1.723 1.974 1.505 C 1.974 1.291 1.956 1.122 1.921 0.998 C 1.885 0.869 1.826 0.778 1.743 0.723 C 1.66 0.669 1.541 0.642 1.387 0.642 C 1.237 0.642 1.118 0.669 1.031 0.723 C 0.949 0.778 0.889 0.869 0.854 0.998 C 0.818 1.122 0.8 1.291 0.8 1.505 C 0.8 1.723 0.814 1.9 0.842 2.036 C 0.874 2.168 0.931 2.266 1.014 2.328 C 1.097 2.386 1.221 2.415 1.387 2.415 Z" fill="rgb(255, 255, 255)" height="3.057263157894756px" id="hVOAJWBR_" transform="translate(24.216 2.444)" width="2.7804678362571735px"/><path d="M 0 2.993 L 0 0.064 L 0.789 0.064 L 0.789 0.251 C 0.852 0.212 0.929 0.175 1.02 0.14 C 1.111 0.101 1.205 0.068 1.304 0.041 C 1.407 0.014 1.506 0 1.601 0 C 1.877 0 2.091 0.049 2.241 0.146 C 2.395 0.239 2.504 0.395 2.567 0.613 C 2.63 0.827 2.662 1.114 2.662 1.476 L 2.662 2.993 L 1.867 2.993 L 1.867 1.517 C 1.867 1.315 1.855 1.153 1.832 1.033 C 1.808 0.908 1.763 0.819 1.695 0.764 C 1.628 0.71 1.529 0.683 1.399 0.683 C 1.328 0.683 1.253 0.69 1.174 0.706 C 1.099 0.718 1.026 0.735 0.954 0.758 C 0.887 0.782 0.832 0.805 0.789 0.828 L 0.789 2.993 Z" fill="rgb(255, 255, 255)" height="2.993099415204677px" id="k6aC5HsJY" transform="translate(27.596 2.444)" width="2.6617543859649118px"/><path d="M 1.316 3.057 C 0.988 3.057 0.727 3.003 0.533 2.894 C 0.344 2.785 0.207 2.62 0.124 2.398 C 0.042 2.176 0 1.898 0 1.564 C 0 1.202 0.051 0.906 0.154 0.677 C 0.261 0.447 0.415 0.278 0.616 0.169 C 0.818 0.056 1.067 0 1.363 0 C 1.802 0 2.132 0.109 2.353 0.327 C 2.579 0.545 2.691 0.889 2.691 1.359 L 2.656 1.791 L 0.794 1.791 C 0.798 2.009 0.844 2.172 0.931 2.281 C 1.018 2.39 1.168 2.445 1.381 2.445 C 1.504 2.445 1.638 2.443 1.784 2.439 C 1.931 2.431 2.075 2.423 2.217 2.415 C 2.363 2.408 2.488 2.4 2.591 2.392 L 2.609 2.935 C 2.51 2.95 2.385 2.968 2.235 2.987 C 2.085 3.007 1.929 3.022 1.767 3.034 C 1.609 3.049 1.458 3.057 1.316 3.057 Z M 0.794 1.295 L 1.903 1.295 C 1.903 1.031 1.86 0.846 1.773 0.741 C 1.69 0.636 1.553 0.583 1.363 0.583 C 1.178 0.583 1.035 0.638 0.937 0.747 C 0.842 0.856 0.794 1.039 0.794 1.295 Z" fill="rgb(255, 255, 255)" height="3.0572631578947593px" id="HWRgQ4Zqc" transform="translate(30.819 2.443)" width="2.691461988304269px"/><path d="M 0 3.985 L 1.031 0 L 2.46 0 L 3.486 3.985 L 2.668 3.985 L 2.442 3.18 L 1.026 3.18 L 0.812 3.985 Z M 1.156 2.532 L 2.324 2.532 L 1.867 0.653 L 1.619 0.653 Z" fill="rgb(255, 255, 255)" height="3.984970760233911px" id="FKU8sIkPM" transform="translate(35.19 1.452)" width="3.48608187134505px"/><path d="M 0 3.985 L 0 0 L 0.818 0 L 0.818 3.985 Z" fill="rgb(255, 255, 255)" height="3.984970760233918px" id="dMjn7rx8Q" transform="translate(39.182 1.452)" width="1px"/></g></svg>)

Executive Summary
An Atypical Travel alert triggered after Microsoft Entra ID observed the user’s last known successful sign-in in Louisiana, followed shortly by two new logins from separate Verizon mobile IPv6 addresses geolocated to Denver. The short time gap between these locations triggered Entra ID’s impossible-travel detection, marking the sequence as potentially suspicious.
Dropzone AI investigated autonomously, enriching user information, IP addresses, and device context across Entra ID, Defender, and Sentinel. Both Denver IPv6 addresses mapped to Verizon’s carrier-grade mobile network, where regional IP shifts are common and often misinterpreted as long-distance travel. Dropzone AI also checked Microsoft Graph calendar data, which showed the user was scheduled for in-person meetings in Denver that day, and all sign-ins came from the user’s known mobile device with MFA enforced.
Taken together, the evidence supported legitimate user travel rather than credential misuse, and Dropzone AI closed the alert within minutes.
This is part of a series that we’re calling the AI SOC Diaries showcasing interesting real-world investigations that the Dropzone AI SOC analyst has performed. Dropzone AI is deployed to 200+ organizations, largely thanks to our MSSP customers that use our AI SOC analyst to provide MDR services to their clients.
Previous AI SOC Diaries entries include:
Investigation #57977 - Legacy Auth, Real Business: The MFA Alert That Didn’t Signal Compromise
Investigation #46671 - Unmasking the Relay: Navigating Alerts Triggered by Anonymized IP Services
Investigation #38175 - How Dropzone AI Cracked a Tricky VPN Logon Alert
Investigation #51541 - Silent Threat or Software Update? Decoding a Suspicious Dell Installer Alert
What Triggered This Atypical Travel Alert Investigation?
The first thing that the Dropzone AI SOC analyst does upon receiving an alert is to orient itself on what type of alert it is, what it is meant to detect, and then come up with hypotheses for why the alert might be malicious or benign. It will then plan an investigation to test those hypotheses. This flow is based on the OSCAR investigative methodology.
In this case, Dropzone AI saw that Microsoft Entra ID triggered an Atypical Travel alert for user b*@.com, a manager at a financial organization.
The alert compared a Monroe, Louisiana sign-in with a subsequent Denver, Colorado session that occurred less than ten minutes later.
At first glance, that velocity suggested impossible travel, but Dropzone AI immediately pivoted through enrichment, historical baselines, and user context before any human analyst touched the queue.
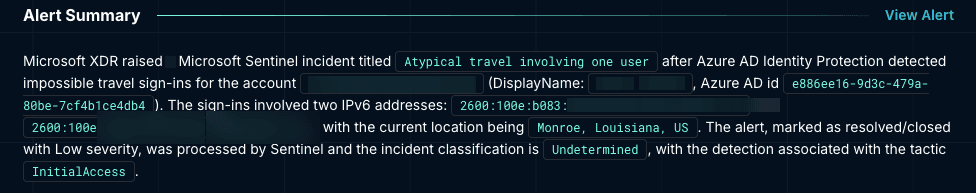
The key question: Was this truly a risky sign-in, or a false positive caused by mobile carrier networks?
How Did Dropzone AI Investigate This Atypical Travel Alert?
Dropzone AI conducted a comprehensive autonomous investigation across multiple data sources and correlation points.
Investigation Process:
Enriched IPv6 addresses to identify Verizon carrier infrastructure
Analyzed user identity through Microsoft Graph
Queried 30 days of historical IP usage in Sentinel and Defender
Validated device posture and MFA compliance from Entra sign-in logs
Correlated tenant-wide environment baselines
Cross-referenced Microsoft Graph calendar data showing scheduled Denver meetings
The investigation resolved the alert as a false positive within minutes without human analyst intervention.
What IPv6 Addresses Triggered the Impossible Travel Detection?
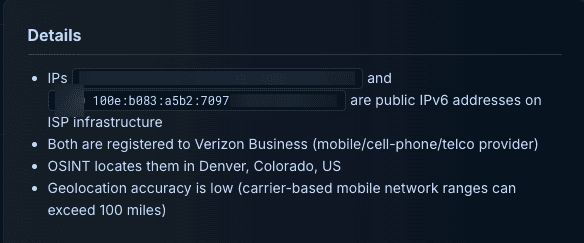
Dropzone AI began by enriching the two IPv6 addresses tied to the new sign-ins:
IPv6 Addresses Analyzed:
2600:100e:b04a:…15a → Verizon Business (Denver, Colorado)
2600:100e:b083:…11c1 → Verizon Business (Denver, Colorado)
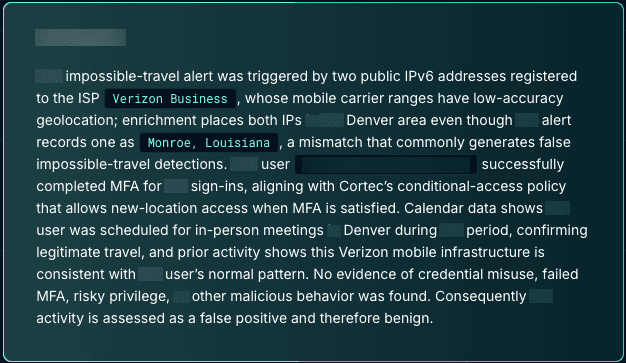
Both addresses resolved to Verizon Business infrastructure in the Denver area, consistent with Verizon’s mobile carrier network.
The preceding successful sign-in was geolocated by Microsoft’s telemetry to Monroe, Louisiana. When the user authenticated again from Denver roughly ten minutes later, Entra ID classified the sequence as Atypical Travel.
Because mobile IPv6 ranges, especially from carriers like Verizon, often rotate across regional gateways, geolocation changes of this kind can appear more dramatic than they are. Dropzone AI treated the distance signal as uncertain pending additional context.
AI Analyst Reasoning: Dropzone AI identified the Denver IPv6 addresses as Verizon Business ranges typical of carrier-grade mobile networks, a nuance that often weakens geolocation-based risk scoring. It therefore interpreted the Louisiana-to-Denver movement as a low-confidence geo-infeasibility signal until supported by further evidence.
What User Identity Context Did Dropzone AI Analyze?
Dropzone AI turned to the user’s Microsoft Graph profile, establishing the user’s identity posture and baseline configuration before weighing the sign-ins.
User Profile Analysis:
Standard, non-privileged user (b*@.com)
Assigned the firm’s Managing Director role
MFA fully registered with strong authentication methods in place
No PIM activations in the week leading up to the alert
Group membership aligned with organizational baseline
SSPR enrollment properly configured
No elevated risk indicators in user configuration
All profile attributes aligned with the organization’s normal executive baseline, suggesting no elevated identity risk.
Why Did Historical IP Analysis Change the Risk Assessment?
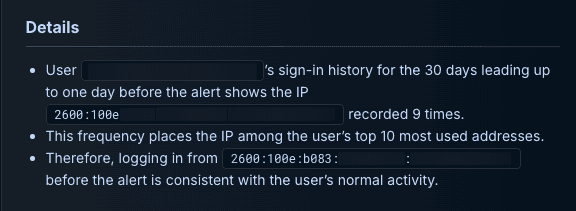
Dropzone AI ran parallel queries across Sentinel and Defender for the previous 30 days to establish historical IP usage patterns.
Historical IP Findings:
The …15a IP address was first-seen with no prior logins
The …11c1 IP address appeared nine times, ranking among the user’s top 10 IPs
The user’s typical IP mix comprised:
Mobile carriers (Verizon, CenturyLink)
Travel-related business networks (hotel and conference Wi-Fi)
Hinge: The repeat use of …11c1 reframed the “new location” hypothesis. In true positive impossible-travel cases, one IP typically reflects real user behavior while the other belongs to the attacker. Here, the historical pattern showed the Denver IP had been used legitimately before, making the Louisiana-to-Denver shift more consistent with normal mobile IP rotation than with credential compromise.

How Did Device Identity and MFA Validation Confirm Legitimacy?
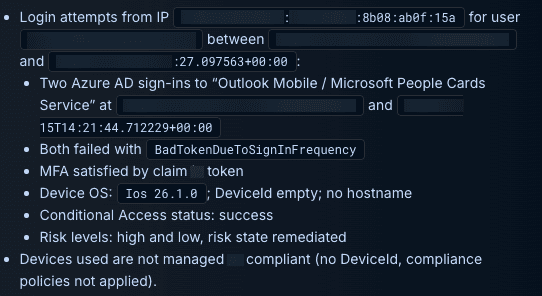
Dropzone AI then pulled device and session details from Entra’s AADSignInEventsBeta logs to validate device consistency and authentication methods.
Device and Session Analysis:
Both sign-ins originated from the user’s personal iOS device running version 26.1.0
Standard MSAL user agent for Outlook Mobile
MFA satisfied through token-based authentication
Device identity aligned with historical patterns
Device was unmanaged and non-compliant (typical for BYOD mobile usage)
Sign-ins targeted expected workloads:
Outlook Mobile
Microsoft People Cards Service
Each attempt failed with BadTokenDueToSignInFrequency, a routine signal that the session token had expired and needed reauthentication rather than anything suggestive of credential misuse.
AI Analyst Reasoning: Dropzone AI correlated successful MFA, consistent device identity, and expected application usage, finding no signs of password failure, replay behavior, or token misuse. The sessions matched normal user activity, not an intrusion attempt.
Why Was Tenant-Wide Environment Analysis Critical?
To understand whether the IPv6 addresses represented shared infrastructure or something tied specifically to the user, Dropzone AI pivoted to tenant-wide sign-in logs.
Environment Correlation Findings:
Only a single account (b*@.com) had ever appeared with either of the Denver IPv6 addresses
No other users in the tenant accessed these IP addresses
What This Ruled Out:
Common shared environments such as hotel Wi-Fi
Corporate proxies or VPN endpoints
Cloud-hosted egress points
Attacker-operated infrastructure appearing across multiple users
Instead, the pattern pointed to a personal mobile connection associated only with this user’s device, supporting the legitimate travel hypothesis.
How Did Calendar Data Verify Physical Travel?
Dropzone AI’s AI SOC analyst doesn’t just use security tools to investigate alerts. It can use business systems as well, such as Microsoft 365 and Google Workspace. This allows it to scan emails to verify legitimate business relationships or check people’s calendars, as was the case here.
To verify physical location context for the user, Dropzone AI then pivoted into Microsoft Graph calendar events for the 24 hours surrounding the alert.
Calendar Verification:
User had multiple in-person meetings scheduled in Denver
Meetings included sessions at the Four Seasons Hotel Denver
Events tied to a private-equity summit
Schedule aligned cleanly with the sign-in locations and timing
This provided external confirmation that the user was physically in Denver during the alert window.
Hinge: Calendar data independently verified the user’s presence in Denver, closing the loop between physical travel context and the sign-in telemetry.
What Was the Final Alert Disposition?
Classification: Benign, normal travel behavior
Priority: Closed / Informational
Supporting Evidence:
All sign-ins passed MFA and conditional-access checks
Both IPv6 addresses were mobile carrier endpoints frequently mis-geolocated
Calendar, device, and historical patterns confirmed legitimate activity by the same user traveling in the U.S.
The “impossible travel” alert was a false positive, resolved automatically without human escalation.
What Does This Investigation Demonstrate About Autonomous Analysis?
This case illustrates how Dropzone AI’s automated analysis moves beyond enrichment to contextual reasoning.
Key Capabilities Demonstrated:
Interpreted carrier network behavior rather than accepting geolocation at face value
Weighted uncertain signals based on multiple corroborating data points
Verified physical travel through independent calendar evidence
Applied measured judgment across cross-domain context
It didn’t just collect data. It interpreted it, recognizing carrier network behavior, weighting uncertain signals, and verifying physical travel through corroborating evidence.
By combining cross-domain context with measured judgment, Dropzone AI resolved the alert autonomously and with high confidence, reducing the manual triage effort that this type of case typically demands.
The Result: When automation applies reasoning instead of reaction, security teams gain both speed and trust in their decisions.
See Dropzone AI in Action
Experience autonomous investigation that resolves impossible travel alerts in minutes, not hours. Dropzone AI analyzes IPv6 geolocation, validates device identity, correlates historical patterns, and verifies calendar context across Microsoft Entra ID, Sentinel, Defender, and Graph - eliminating false positives without manual triage.
Ready to reduce alert investigation time by 90%?Schedule a demo to see how autonomous investigations achieves 100% alert coverage while freeing your analysts for strategic threat hunting.
If you’re not ready to talk to us yet, we also have a self-guided demo that allows you to explore a live Dropzone AI environment.
What Technical Concepts Underpin This Investigation?
Six key technical concepts underpin this investigation and explain how Dropzone AI distinguished legitimate travel from potential credential compromise.
Carrier-Grade IPv6 Rotation
Mobile carriers such as Verizon frequently assign IPv6 addresses from large, regional pools that shift as devices move between towers or routing gateways. These rotations can make IP geolocation appear to jump hundreds of miles, even when the user is in the same city.
Geolocation as an Estimation Signal
IP geolocation in Entra ID reflects the provider’s registered routing location, not the user’s physical position. Mobile and cloud networks often misrepresent true location, making distance-based detections noisy without supporting context.
Conditional Access Evaluation
A ConditionalAccessStatus = Success result confirms that all applicable policies, including MFA, were validated and satisfied. It signals enforcement, not policy bypass, and is a strong indicator of legitimate authentication.
Historical IP Baselining
Repeated use of the same IP or provider range is a meaningful trust signal. When an address that initially appears “new” actually shows up in a user’s historical logs, especially mobile carrier ranges, it often reframes travel anomalies as expected behavior.
Unmanaged BYOD Devices
Unmanaged iOS and mobile devices are common in many environments. Device management status is a helpful data point, but in isolation it is not an indicator of compromise. Device identity, MFA, and activity alignment carry more weight.
Calendar-Driven Context Validation
Correlating sign-ins with Microsoft Graph calendar events provides independent physical context. When scheduled in-person meetings align with sign-in locations, they strengthen the confidence of benign travel determinations.
" width="32px"><path d="M 10 11.4 L 0 1.4 L 1.4 0 L 10 8.6 L 18.6 0 L 20 1.4 Z" fill="rgb(0, 0, 0)" height="11.400000000000006px" id="WzVcCPzSg" transform="translate(6 10.5)" width="20px"/><path d="M 0 0 L 32 0 L 32 32 L 0 32 Z" fill="transparent" height="32px" id="JnWsCmB6z" width="32px"/></g></svg>)


